Microsoft Administering Windows Server AZ-802 Dumps in PDF

Free Microsoft AZ-802 Real Questions (page: 3)


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
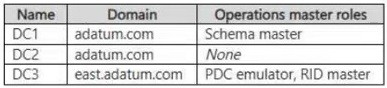
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.
Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
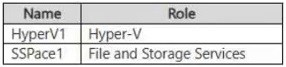
The adatum.com domain contains the servers shown in the following table.
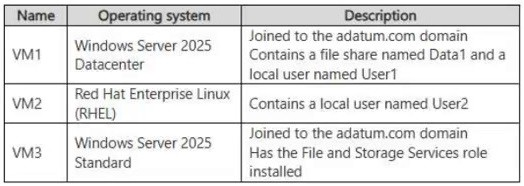
HyperV1 contains the virtual machines shown in the following table.
All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
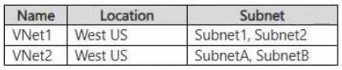
The subscription contains the virtual networks shown in the following table.
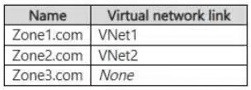
The subscription contains the Azure Private DNS zones shown in the following table.
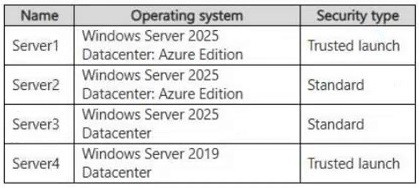
The subscription contains the virtual machines shown in the following table.
All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Sites and Services, you right-click Default-First-Site-Name in the console tree, and then select Properties.
Does this meet the goal?

  1. Yes
  2. No

Answer(s): B

Explanation:

The properties of Default-First-Site-Name do not identify the domain’s PDC emulator. The PDC emulator is a domain-level FSMO role and can be identified through tools such as Active Directory Users and Computers, Active Directory Domains and Trusts, or PowerShell commands such as Get-ADDomain.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
The domain contains a user named User1 and two global security groups named Group1 and Group2. User1 is a member of both groups.
A Group Policy Object (GPO) named GPO1 is linked to the domain. GPO1 contains the following User Configuration preference items.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: No
No, drive S will not be mapped.
Failed Targeting: Item-level targeting requires both membership in the first global group and an IP address in the range of 10.10.0.0 to 10.10.255.255.
IP Mismatch: The sign-in IP address (10.20.5.20) is outside the specified range. Because the targeting rule uses an AND condition, the entire filter evaluates to false.
Removal Rule: The option Remove this item when it is no longer valid is selected, meaning the preference item will not apply or will be removed if the conditions are not met.
Box 2: Yes
Yes, the user will not have driven S in File Explorer after signing in.
Targeting Condition Fails: Item-level targeting requires both the first global group and the IP address range 10.10.0.0 through 10.10.255.255. Removing the user from Group1 makes this targeting rule false.
Removal Option Active: The setting "Remove this item when it is no longer valid" is selected.
When targeting fails, the Group Policy engine actively removes the configuration.
Continuous Evaluation: "Apply once and do not reapply" is disabled. This means the preference re-evaluates the targeting rules at every sign-in and policy update, enforcing the removal when conditions are no longer met.
Box 3: Yes
Yes, the shortcut is created once and never reapplied or recreated on future Group Policy refreshes.
Targeting is met: The targeting uses an OR condition (member of the second global group OR local file exists). Because the user is in the second global group, the targeting condition evaluates to true even though the local file C:\Program files\SalesApp\SalesApp.exe does not exist on the client computer.
Apply once setting: The option Apply once and do not reapply is selected for the shortcut. Group Policy Preferences applies the setting a single time and ignores it on all subsequent policy refreshes.


Reference:

https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/manage/understand-security-groups


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the domain controllers shown in the following table.

You have a partner organization that has an AD DS forest named fabrikam.com.
You create a trust relationship between contoso.com and fabrikam.com.
You need to configure selective authentication for the trust relationship.
Which domain controller should be granted permissions to fabrikam.com?

  1. DC1
  2. DC2
  3. DC3
  4. DC4

Answer(s): D

Explanation:

For selective authentication across a forest trust, the PDC emulator in the trusted forest must be permitted to authenticate to the domain controllers in the trusting forest so that trust-related authentication can function correctly. DC4 holds the PDC emulator role.


Reference:

https://learn.microsoft.com/en-us/troubleshoot/windows-server/windows-security/windows-updates-add-new-ntlm-pass-through-authentication-protections


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) domain. The network also contains 20 domain controllers, 100 member servers, and 10,000 client computers.
You have a Group Policy Object (GPO) named GPO1 that contains Group Policy preferences.
You plan to link GPO1 to the domain.
You need to ensure that the preferences in GPO1 apply only to domain member servers and NOT to domain controllers or client computers. All the other Group Policy settings in GPO1 must apply to all the computers. The solution must minimize administrative effort.
Which type of item-level targeting should you use?

  1. Security Group
  2. Environment Variable
  3. Domain
  4. Operating System

Answer(s): D

Explanation:

Operating System item-level targeting lets you select Server as the computer role, limiting the preference items to member servers. Item-level targeting affects only the configured preference items, so the other settings in GPO1 continue to apply to all computers in the domain.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Domains and Trusts, you right-click Active Directory Domains and Trusts in the console tree, and then select Operations Master.
Does this meet the goal?

  1. Yes
  2. No

Answer(s): B

Explanation:

Active Directory Domains and Trusts displays the holder of the Domain Naming Master FSMO role. The PDC emulator is a domain-level FSMO role and is not identified from that Operations Master dialog.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. Contoso.com contains two organizational units (OUs) named OU1 and OU2. OU1 has Block Inheritance enabled.
Contoso.com has the Group Policy Objects (GPOs) shown in the following table.

Which GPOs will apply to users and computers in OU1 and OU2? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


GPO2 and Default Domain Policy only
GPO1 and Default Domain Policy only
OU1’s Block Inheritance prevents inheritance of GPO1, but the enforced Default Domain Policy still applies. GPO2 also applies because it is linked directly to OU1. OU2 inherits both domain-linked policies, GPO1 and Default Domain Policy. Its GPO3 link is disabled, so GPO3 does not apply.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

DRAG DROP (Drag and Drop is not supported)
You deploy a single-domain Active Directory Domain Services (AD DS) forest named contoso.com.
You deploy a server to the domain and configure the server to run a service.
You need to ensure that the service can use a group managed service account (gMSA) to authenticate.
Which three PowerShell cmdlets should you run in sequence? To answer, move the appropriate cmdlets from the list of cmdlets to the answer area and arrange them in the correct order.
Select and Place:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


1. Add-KdsRootKey
2. New-ADServiceAccount
3. Install-ADServiceAccount
A KDS root key must first exist so Active Directory can generate and manage gMSA passwords. The gMSA is then created in AD DS, after which it is installed on the server that will run the service.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains five sites. Each site contains a single domain controller.
You need to minimize replication delays between the domain controllers.
How should you complete the PowerShell cmdlet? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Get-ADReplicationSiteLink -Filter * | Set-ADObject -Replace @{'options'=1}
The command retrieves all replication site links and enables intersite change notifications by setting their options attribute to 1. This triggers replication when changes occur instead of waiting for the periodic replication interval, reducing delays between sites.


Reference:

https://learn.microsoft.com/en-us/powershell/module/activedirectory/set-adreplicationsitelink?view= windowsserver2025-ps


Share your comments for Microsoft AZ-802 exam with other users:

A
Aish
10/11/2023 5:27:00 AM

want to pass exm.

A
Anonymous
6/12/2023 7:23:00 AM

are the answers correct?

K
Kris
7/7/2023 9:43:00 AM

good morning, could you please upload this exam again, i need it to test my knowledge in sd-wan with version 7.0.

M
Meghraj mali
10/7/2023 1:47:00 PM

very nice question

N
Noel
11/1/2022 9:14:00 PM

i have learning disability and this exam dumps allowed me to focus on the actual questions and not worry about notes and the those other study materials.

J
Jas
10/25/2023 6:01:00 PM

165 should be apt

N
Neetu
6/22/2023 8:41:00 AM

please upload the dumps, real need of them

M
Mark
10/24/2023 1:34:00 AM

any recent feeedback?

G
Gopinadh
8/9/2023 4:05:00 AM

question number 2 is indicating you are giving proper questions. observe and change properly.

S
Santhi
1/1/2024 8:23:00 AM

passed today.40% questions were new.litwere case study,lots of new questions on afd,ratelimit,tm,lb,app gatway.got 2 set series of questions which are not present here.questions on azure cyclecloud, no.of vnet/vms required for implimentation,blueprints assignment/management group etc

R
Raviraj Magadum
1/12/2024 11:39:00 AM

practice test

S
sivaramakrishnan
7/27/2023 8:12:00 AM

want the dumps for emc content management server programming(cmsp)

A
Aderonke
10/23/2023 1:52:00 PM

brilliant and helpful

A
Az
9/16/2023 2:43:00 PM

q75. azure files is pass

K
ketty
11/9/2023 8:10:00 AM

very helpful

S
Sonail
5/2/2022 1:36:00 PM

thank you for these questions. it helped a lot.

S
Shariq
7/28/2023 8:00:00 AM

how do i get the h12-724 dumps

A
adi
10/30/2023 11:51:00 PM

nice data dumps

E
EDITH NCUBE
7/25/2023 7:28:00 AM

answers are correct

R
Raja
6/20/2023 4:38:00 AM

good explanation

B
BigMouthDog
1/22/2022 8:17:00 PM

hi team just want to know if there is any update version of the exam 350-401

F
francesco
10/30/2023 11:08:00 AM

helpful on 2017 scrum guide

A
Amitabha Roy
10/5/2023 3:16:00 AM

planning to attempt for the exam.

P
Prem Yadav
7/29/2023 6:20:00 AM

pleaseee upload

A
Ahmed Hashi
7/6/2023 5:40:00 PM

thanks ly so i have information cia

M
mansi
5/31/2023 7:58:00 AM

hello team, i need sap qm dumps for practice

J
Jamil aljamil
12/4/2023 4:47:00 AM

it’s good but not senatios based

C
Cath
10/10/2023 10:19:00 AM

q.119 - the correct answer is b - they are not captured in an update set as theyre data.

P
P
1/6/2024 11:22:00 AM

good matter

S
surya
7/30/2023 2:02:00 PM

please upload c_sacp_2308

S
Sasuke
7/11/2023 10:30:00 PM

please upload the dump. thanks very much !!

V
V
7/4/2023 8:57:00 AM

good questions

T
TTB
8/22/2023 5:30:00 AM

hi, could you please update the latest dump version

T
T
7/28/2023 9:06:00 PM

this question is keep repeat : you are developing a sales application that will contain several azure cloud services and handle different components of a transaction. different cloud services will process customer orders, billing, payment, inventory, and shipping. you need to recommend a solution to enable the cloud services to asynchronously communicate transaction information by using xml messages. what should you include in the recommendation?

AI Tutor 👋 I’m here to help!