Microsoft Administering Windows Server AZ-802 Dumps in PDF

Free Microsoft AZ-802 Real Questions (page: 2)


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
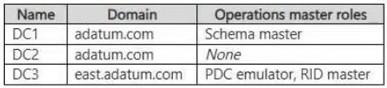
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.
Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
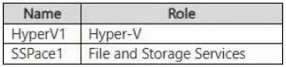
The adatum.com domain contains the servers shown in the following table.
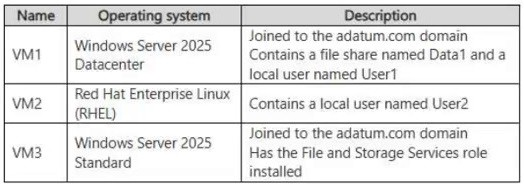
HyperV1 contains the virtual machines shown in the following table.
All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
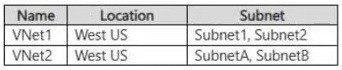
The subscription contains the virtual networks shown in the following table.
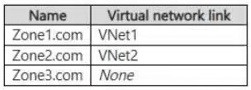
The subscription contains the Azure Private DNS zones shown in the following table.
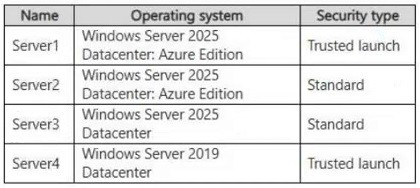
The subscription contains the virtual machines shown in the following table.
All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

DRAG DROP (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a user named User1.
You need to use PowerShell to create a new global security group named Group1 that contains User1.
How should you complete the script? To answer, drag the appropriate cmdlets to the correct targets. Each cmdlet may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
Note: Each correct selection is worth one point.
Select and Place:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


New-ADGroup
Add-ADGroupMember
New-ADGroup creates the new global security group. Add-ADGroupMember then adds User1 directly to Group1.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

DRAG DROP (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) forest.
The forest contains a root domain named contoso.com and a child domain named branch.contoso.com. The domain contains a domain controller named DC1 that holds all the domain-wide FSMO roles.
DC1 fails and cannot be restored, causing the following issues:
● Recent password changes are NOT recognized immediately during sign-ins to contoso.com.
● Domains cannot be added or removed from the forest.
You need to seize the minimum domain-wide FSMO roles on a domain controller named DC2 to resolve the issues.
Which role should you seize for each issue? To answer, drag the appropriate roles to the correct issue. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
Note: Each correct selection is worth one point.
Select and Place:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: PDC Emulator
The PDC Emulator (Primary Domain Controller Emulator) FSMO role is appropriate.
Password Processing: The PDC Emulator processes password changes and preferentially receives urgent replication of password updates from other domain controllers.
Authentication Forwarding: If a sign-in attempt fails on a local domain controller because a recent password change has not yet replicated there, that domain controller forwards the authentication request directly to the PDC Emulator to verify against the latest password.
Box 2: Domain naming master
The Domain Naming Master role must be chosen and seized to fix this issue.
Forest-wide scope: It is one of two unique forest-wide FSMO roles.
Domain operations: It controls the addition or removal of domains in an Active Directory forest.
Failure impact: When the domain controller holding this role fails and cannot be recovered, no new domains can be added and existing domains cannot be removed until the role is seized on a working second domain controller


Reference:

https://learn.microsoft.com/en-us/troubleshoot/windows-server/active-directory/view-transfer-fsmo-roles


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domains Services (AD DS) forest named adatum.com. Adatum.com contains the users shown in the following table.

You deploy a workgroup server named RODC1 that runs Windows Server. RODC1 contains a user named User4 that is a member of the local Administrators group.
You pre-create a read-only domain controller (RODC) account named RODC1 in east.adatum.com and delegate RODC installation and administration permissions to User3.
You sign-in to RODC1 as User4.
Which credentials can be used to promote RODC1 to a RODC in east.adatum.com?

  1. User3 only
  2. User3 and User1 only
  3. User3 and User2 only
  4. User1, User2, and User3

Answer(s): D

Explanation:

User1 has forest-wide privileges through Enterprise Admins, and User2 has administrative privileges in east.adatum.com through Domain Admins. User3 can complete the staged RODC installation because installation permissions were explicitly delegated to that account. Any of these credentials can therefore attach RODC1 to its pre-created account and complete promotion.


Reference:

https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/deploy/install-active-directory-dom ain-services--level-100-


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest root domain contains a server named server1.contoso.com.
A two-way forest trust exists between the contoso.com forest and an AD DS forest named fabrikam.com. The fabrikam.com forest contains 10 child domains.
You need to ensure that only the members of a group named fabrikam\Group1 can authenticate to server1.contoso.com.
What should you do first?

  1. Enable SID filtering for the trust.
  2. Enable Selective authentication for the trust.
  3. Change the trust to a one-way external trust.
  4. Add fabrikam\Group1 to the local Users group on server1.contoso.com.

Answer(s): B

Explanation:

Selective authentication lets you explicitly control which users from a trusted forest can authenticate to particular computers. Enable it for access from fabrikam.com to contoso.com, then grant fabrikam\Group1 the Allowed to authenticate permission on Server1’s computer object.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains the Active Directory Domain Services (AD DS) forests shown in the following table.

You need to configure trust relationships as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: No
No, contoso.com users cannot access resources in adatum.com after both trusts are configured.
Forest Trusts are not transitive across multiple forests: While a forest trust allows transitivity within the participant forests (covering all their child domains), the transitivity stops at the forest boundary. It does not automatically cross over into a third forest.
The Trust Chain Breaks: In the configuration, you have established separate trust relationships linking contoso.com ↔ fabrikam.com and fabrikam.com ↔ adatum.com. Because trust cannot route implicitly through fabrikam.com from one external forest to another, there is no valid authentication path between contoso.com and adatum.com.
Box 2: Yes
Yes, a single two-way forest trust between contoso.com and fabrikam.com satisfies the first required trust relationship.
By definition, a forest trust is inherently transitive across all child domains within the involved forests.
When you establish a two-way forest trust between the root domains (contoso.com and fabrikam.com), the trust relationship automatically extends to all domains inside both forest infrastructures.
This allows users from any domain in the contoso.com forest (contoso.com, europe.contoso.com, and asia.contoso.com) to be authenticated and access authorized resources in any domain in the fabrikam.com forest (fabrikam.com and research.fabrikam.com), and vice versa. No separate domain-level trusts are required to achieve this scope of access.
Box 3: Yes
Yes, a one-way external trust in which research.fabrikam.com trusts adatum.com fully satisfies the second trust relationship requirement.
Direction of Trust vs. Direction of Access: In Active Directory, trust flows in one direction while resource access flows in the exact opposite direction. Setting up a one-way trust where research.fabrikam.com (the resource domain) trusts adatum.com (the user domain) means that authentication requests are passed to adatum.com. As a result, users from adatum.com are allowed to authenticate and access authorized resources inside research.fabrikam.com.
Non-Transitivity of External Trusts: External trusts are explicitly non-transitive. This ensures that trust and access are strictly limited to the two specific domains involved (adatum.com and research.fabrikam.com). Users from adatum.com will not gain unauthorized access to the parent domain (fabrikam.com), keeping the rest of the forest isolated and secure.


Reference:

https://learn.microsoft.com/en-us/entra/identity/domain-services/concepts-forest-trust


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com.
You have an Azure virtual network named VNet1 that is connected to the on-premises network by using a Site-to-Site (S2S) VPN.
VNet1 contains a domain-joined virtual machine named VM1 that hosts an application named App1.
App1 uses Kerberos authentication and updates objects in AD DS. An Azure Firewall filters communication from VM1 to the domain controllers in contoso.com.
You need to deploy domain controllers to VNet1. The solution must support the requirements of VM1 and provide domain controller redundancy in Azure.
What should you deploy?

  1. two writable domain controller virtual machines across availability zones
  2. two read-only domain controller (RODC) virtual machines across availability sets
  3. two writable domain controller virtual machines, each in a distinct Azure region
  4. two read-only domain controller (RODC) virtual machines, each in a distinct Azure region

Answer(s): A

Explanation:

Two writable domain controller virtual machines across availability zones should be deployed.
Writable Requirement: The application running on the virtual machine updates objects in Active Directory Domain Services (AD DS). Read-only domain controllers (RODCs) cannot process write operations or object updates, which means an RODC would fail to support the application's write requirements.
Redundancy and High Availability: Availability zones provide a high-availability offering that protects your applications and data from datacenter failures, making them superior to availability sets for domain controller redundancy in Azure.


Reference:

https://learn.microsoft.com/en-us/azure/architecture/example-scenario/identity/adds-extend-domain


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) forest.
The forest contains a root domain named contoso.com and a child domain named branch.contoso.com.
The forest contains the domain controllers shown in the following table.

You discover that cross-domain object references in contoso.com fail to update for objects in branch.contoso.com.
You need to modify the FSMO role placement. The solution must minimize administrative changes.
What should you do?

  1. Transfer the infrastructure master role for contoso.com from DC1 to DC2.
  2. Transfer the PDC emulator role for contoso.com from DC1 to DC2.
  3. Transfer the schema master role from DC1 to DC2.
  4. Transfer the infrastructure master role for branch contoso.com from DC4 to DC3.
  5. Transfer the domain naming master role from DC1 to DC2.

Answer(s): A

Explanation:

Transfer the infrastructure master role in contoso.com from DC1 to DC2.
The Conflict: In a multi-domain forest where not all domain controllers are global catalog servers, the Infrastructure Master (IM) role must not be placed on a Global Catalog (GC) server.
The Symptom: DC1 in contoso.com holds the IM role and is also a GC server. Because a GC holds a partial replica of all objects in the forest, an IM on a GC assumes its data is always up-to-date and fails to detect or replicate cross-domain reference updates from branch.contoso.com.
Action to take with low administrative effort
Move the Role: Transfer only the Infrastructure Master role in the root domain (contoso.com) from DC1 to DC2.
DC2 is ideal because it resides in contoso.com and is not a global catalog server, which directly satisfies Active Directory best practices and resolves the cross-domain update failure.


Reference:

https://vinitpandey.com/2016/09/05/why-global-catalog-server-and-infrastructure-operation-master-shouldnt-be -on-same-server/


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains the domains shown in the following exhibit.

You need to establish trust relationships as shown in the following exhibit.

Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Trust1: Shortcut trust only
Trust2: Forest trust or external trust only
Trust1 connects two domains within the same forest, so a shortcut trust can be used to optimize authentication between them. Trust2 connects domains in separate forests; a forest trust can establish transitive trust between the forests, while an external trust can establish a nontransitive trust between the specified domains.


Share your comments for Microsoft AZ-802 exam with other users:

S
Stephen
8/4/2023 9:08:00 PM

please upload cima e2 managing performance dumps

H
hp
6/16/2023 12:44:00 AM

wonderful questions

P
Priyo
11/14/2023 2:23:00 AM

i used this site since 2000, still great to support my career

J
Jude
8/29/2023 1:56:00 PM

why is the answer to "which of the following is required by scrum?" all of the following stated below since most of them are not mandatory? sprint retrospective. members must be stand up at the daily scrum. sprint burndown chart. release planning.

M
Marc blue
9/15/2023 4:11:00 AM

great job. hope this helps out.

A
Anne
9/13/2023 2:33:00 AM

upload please. many thanks!

P
pepe el toro
9/12/2023 7:55:00 PM

this is so interesting

A
Antony
11/28/2023 12:13:00 AM

great material thanks

T
Thembelani
5/30/2023 2:22:00 AM

anyone who wrote this exam recently

P
P
9/16/2023 1:27:00 AM

ok they re good

J
Jorn
7/13/2023 5:05:00 AM

relevant questions

A
AM
6/20/2023 7:54:00 PM

please post

N
Nagendra Pedipina
7/13/2023 2:22:00 AM

q:42 there has to be a image in the question to choose what does it mean from the options

B
BrainDumpee
11/18/2023 1:36:00 PM

looking for cphq dumps, where can i find these for free? please and thank you.

S
sheik
10/14/2023 11:37:00 AM

@aarun , thanks for the information. it would be great help if you share your email

R
Random user
12/11/2023 1:34:00 AM

1z0-1078-23 need this dumps

L
labuschanka
11/16/2023 6:06:00 PM

i gave the microsoft azure az-500 tests and prepared from this site as it has latest mock tests available which helped me evaluate my performance and score 919/1000

M
Marianne
10/22/2023 11:57:00 PM

i cannot see the button to go to the questions

S
sushant
6/28/2023 4:52:00 AM

good questions

A
A\MAM
6/27/2023 5:17:00 PM

q-6 ans-b correct. https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-cli-quick-start/use-the-cli/commit-configuration-changes

U
unanimous
12/15/2023 6:38:00 AM

very nice very nice

A
akminocha
9/28/2023 10:36:00 AM

please help us with 1z0-1107-2 dumps

J
Jefi
9/4/2023 8:15:00 AM

please upload the practice questions

T
Thembelani
5/30/2023 2:45:00 AM

need this dumps

A
Abduraimov
4/19/2023 12:43:00 AM

preparing for this exam is overwhelming. you cannot pass without the help of these exam dumps.

P
Puneeth
10/5/2023 2:06:00 AM

new to this site but i feel it is good

A
Ashok Kumar
1/2/2024 6:53:00 AM

the correct answer to q8 is b. explanation since the mule app has a dependency, it is necessary to include project modules and dependencies to make sure the app will run successfully on the runtime on any other machine. source code of the component that the mule app is dependent of does not need to be included in the exported jar file, because the source code is not being used while executing an app. compiled code is being used instead.

M
Merry
7/30/2023 6:57:00 AM

good questions

V
VoiceofMidnight
12/17/2023 4:07:00 PM

Delayed the exam until December 29th.

U
Umar Ali
8/29/2023 2:59:00 PM

A and D are True

V
vel
8/28/2023 9:17:09 AM

good one with explanation

G
Gurdeep
1/18/2024 4:00:15 PM

This is one of the most useful study guides I have ever used.

AI Tutor 👋 I’m here to help!