Microsoft Administering Windows Server AZ-802 Dumps in PDF

Free Microsoft AZ-802 Real Questions (page: 7)


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
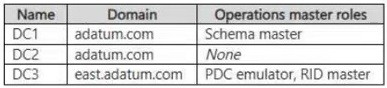
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.
Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
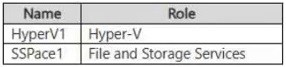
The adatum.com domain contains the servers shown in the following table.
HyperV1 contains the virtual machines shown in the following table.
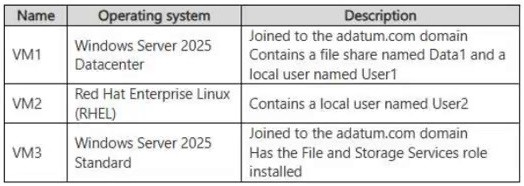
All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
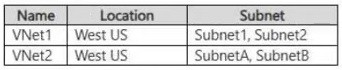
The subscription contains the virtual networks shown in the following table.
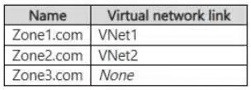
The subscription contains the Azure Private DNS zones shown in the following table.
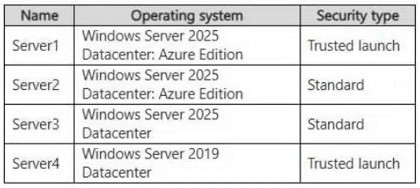
The subscription contains the virtual machines shown in the following table.
All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains two domain controllers named DC1 and DC2.
You plan to perform the following actions:
● Add two domain controllers named DC3 and DC4 to contoso.com.
● Configure DC3 as a domain controller and DC4 as a read-only domain controller (RODC).
● Add a new child domain named east.contoso.com that will be hosted on a domain controller named DC5.
You need to use the install from media (IFM) option, whenever possible.
What can you use to prepare the IFM data, and which domain controllers can be promoted by using the IFM option? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


ntdsutil.exe
DC3 and DC4 only
Ntdsutil creates IFM media for both writable domain controllers and RODCs. DC3 and DC4 can use the appropriate media because they join the existing contoso.com domain. IFM cannot install the first domain controller in a new domain, so DC5 is ineligible.


Reference:

https://learn.microsoft.com/en-us/previous-versions/windows/it-pro/windows-server-2012-r2-and-20 12/cc732530%28v%3Dws.11%29
https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/deploy/install-active-directory-domain-services --level-100-


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain.
The domain contains a file server named FS1 that hosts a file share named Finance. The domain contains an organizational unit (OU) named OU1 and a global security group named Group1.
A Group Policy Object (GPO) named GPO1 is linked to OU1.
You need to configure a Group Policy preferences item that maps drive F to \\FS1\Finance for the members of Group1. The item will use Security Group item-level targeting and remove the preferences setting when the setting no longer applies.
The solution must recreate the preferences setting during Group Policy refresh if a user deletes or changes the setting.
What should you configure? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Preference extension: Drive Maps
Action: Replace
The Drive Maps preference extension is used to map drive F to \\FS1\Finance. The Replace action deletes and recreates the mapped drive during Group Policy refresh, ensuring that the required configuration is restored if a user deletes or changes it. It also supports item-level targeting and removal when the preference item no longer applies.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your on-premises network contains an Active Directory Domain Services (AD DS) domain.
You have an Azure subscription.
The AD DS domain contains the domain controllers shown in the following table.

To the Azure subscription, you deploy a virtual machine named DC5 that runs Windows Server 2025.
You plan to promote DC5 to a domain controller by using Install from media (IFM).
You need to create the media for DC5. The solution must minimize the network traffic between the on-premises network and the Azure subscription during the promotion of DC5.
Which domain controller should you use to create the IFM media?

  1. DC1
  2. DC2
  3. DC3
  4. DC4

Answer(s): C

Explanation:

DC3 is the intended choice because it is already in Azure, minimizing transfers between the on-premises network and Azure when preparing and using the IFM media.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From a command prompt, you run netdom.exe query fsmo.
Does this meet the goal?

  1. Yes
  2. No

Answer(s): A

Explanation:

netdom.exe query fsmo displays the servers that currently hold the five FSMO roles in the forest and domain, including the PDC emulator.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

You have an Active Directory Domain Services (AD DS) forest that has the Active Directory Recycle Bin enabled. The forest contains a user named User1.
User1 is accidentally deleted.
You need to restore User1 from the Active Directory Recycle Bin.
What should you use?

  1. Active Directory Users and Computers
  2. Active Directory Domains and Trusts
  3. Active Directory Administrative Center
  4. Active Directory Sites and Services

Answer(s): C

Explanation:

Active Directory Administrative Center provides the graphical interface for viewing deleted objects and restoring them from the Active Directory Recycle Bin when the feature is enabled.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) domain.
You plan to use Active Directory Administrative Center to create a new user named User1.
Which two attributes are required to create User1? Each correct answer presents part of the solution.
Note: Each correct selection is worth one point.

  1. First name
  2. Password
  3. User UPN logon
  4. Profile path
  5. Full name
  6. User SamAccountName logon

Answer(s): E,F

Explanation:

In Active Directory Administrative Center, the required fields for creating a user are Full name and User SamAccountName logon. These identify the directory object and provide the account’s legacy logon name. A password is not required to create the user object; without one, the account remains disabled.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

DRAG DROP (Drag and Drop is not supported)
You have a single-domain Active Directory Domain Services (AD DS) forest named contoso.com that contains two domain controllers named DC1 and DC2. DC1 and DC2 run Windows Server.
You plan to perform an authoritative restore of SYSVOL on DC1.
You isolate DC1 and restore DC1 from a backup.
You need to ensure that SYSVOL on DC1 replicates to DC2.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


1. From Active Directory Users and Computers on DC1, select Advanced Features.
2. For the computer object of DC1, select SYSVOL Subscription and modify the value of the msDFSR-Options attribute.
3. Connect DC1 to the network.
For an authoritative SYSVOL restore using DFS Replication, the restored domain controller must be designated as the authoritative source before it resumes replication. Enabling Advanced Features exposes the SYSVOL Subscription object, where the msDFSR-Options attribute can be configured to mark DC1 as authoritative. DC1 is then reconnected so its restored SYSVOL data can replicate to DC2.


Case Study
Overview:
Company Information
A: Datum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership

A: Datum recently partnered with a company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment

A: Datum AD DS Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.

Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.

HyperV1 contains the virtual machines shown in the following table.

All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces Virtual disks shown in the following table.

Azure Resources

A: Datum has an Azure subscription that contains a Microsoft Entra tenant. Microsoft Entra Connect sync is configured to sync the adatum.com forest with the Microsoft Entra tenant.
The subscription contains the virtual networks shown in the following table.

The subscription contains the Azure Private DNS zones shown in the following table.

The subscription contains the virtual machines shown in the following table.

All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes

A: Datum plans to implement the following changes:
● Sync Data1 to share 1.
● Configure an Azure runbook named Task1.
● Enable Microsoft Entra users to sign in to Server1.
● Create an Azure DNS Private Resolver that has the following configurations:
● Name: Private1
● Region: West US
● Virtual network: VNet1
● Inbound endpoint: SubnetB
● Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements

A: Datum identifies the following technical requirements:
● The data on SSPace1 must be always available.
● DC2 must become the schema master if DC1 fails.
● VM3 must be configured to enable per-folder quotas.
● Trusts must allow access to only the required resources.
● The users in the Marketing OU must have access to storage1.
● Azure Automanage must be used on all supported Azure virtual machines.
● A direct SSH session must be used to manage all the supported virtual machines on HyperV1.

Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a server named Server1.
Server1 hosts an IIS website that has Windows Authentication enabled and Negotiate configured as an authentication provider.
The IIS application pool runs as CONTOSO\WebAppSvc, and Kerberos uses the application pool identity.
You discover that users cannot use Kerberos authentication to access http://server1.contoso.com. A network trace shows that a client computer named Client1 requested a service ticket for HTTP/server1.contoso.com, and the Key Distribution Center (KDC) returned KDC_ERR_S_PRINCIPAL_UNKNOWN.
You need to restore Kerberos authentication. The application pool identity must remain unchanged.
What should you modify?

  1. the time synchronization settings for Client1
  2. the servicePrincipalName attribute of CONTOSO\WebAppSvc
  3. the firewall rule for TCP port 80
  4. the DNS host (A) record for server1.contoso.com
  5. the servicePrincipalName attribute for the computer account of Server1

Answer(s): B

Explanation:

Kerberos requires the HTTP/server1.contoso.com service principal name to be registered on the account that IIS uses for Kerberos authentication. Because the application pool runs as CONTOSO\WebAppSvc and Kerberos uses that application pool identity, the HTTP SPN must be registered on WebAppSvc. The KDC_ERR_S_PRINCIPAL_UNKNOWN error indicates that the KDC cannot locate the requested SPN.


Share your comments for Microsoft AZ-802 exam with other users:

C
Chiranthaka
9/20/2023 11:22:00 AM

very useful!

N
Not Miguel
11/26/2023 9:43:00 PM

for this question - "which three type of basic patient or member information is displayed on the patient info component? (choose three.)", list of conditions is not displayed (it is displayed in patient card, not patient info). so should be thumbnail of chatter photo

A
Andrus
12/17/2023 12:09:00 PM

q52 should be d. vm storage controller bandwidth represents the amount of data (in terms of bandwidth) that a vms storage controller is using to read and write data to the storage fabric.

R
Raj
5/25/2023 8:43:00 AM

nice questions

M
max
12/22/2023 3:45:00 PM

very useful

M
Muhammad Rawish Siddiqui
12/8/2023 6:12:00 PM

question # 208: failure logs is not an example of operational metadata.

S
Sachin Bedi
1/5/2024 4:47:00 AM

good questions

K
Kenneth
12/8/2023 7:34:00 AM

thank you for the test materials!

H
Harjinder Singh
8/9/2023 4:16:00 AM

its very helpful

S
SD
7/13/2023 12:56:00 AM

good questions

K
kanjoe
7/2/2023 11:40:00 AM

good questons

M
Mahmoud
7/6/2023 4:24:00 AM

i need the dumb of the hcip security v4.0 exam

W
Wei
8/3/2023 4:18:00 AM

upload the dump please

S
Stephen
10/3/2023 6:24:00 PM

yes, iam looking this

S
Stephen
8/4/2023 9:08:00 PM

please upload cima e2 managing performance dumps

H
hp
6/16/2023 12:44:00 AM

wonderful questions

P
Priyo
11/14/2023 2:23:00 AM

i used this site since 2000, still great to support my career

J
Jude
8/29/2023 1:56:00 PM

why is the answer to "which of the following is required by scrum?" all of the following stated below since most of them are not mandatory? sprint retrospective. members must be stand up at the daily scrum. sprint burndown chart. release planning.

M
Marc blue
9/15/2023 4:11:00 AM

great job. hope this helps out.

A
Anne
9/13/2023 2:33:00 AM

upload please. many thanks!

P
pepe el toro
9/12/2023 7:55:00 PM

this is so interesting

A
Antony
11/28/2023 12:13:00 AM

great material thanks

T
Thembelani
5/30/2023 2:22:00 AM

anyone who wrote this exam recently

P
P
9/16/2023 1:27:00 AM

ok they re good

J
Jorn
7/13/2023 5:05:00 AM

relevant questions

A
AM
6/20/2023 7:54:00 PM

please post

N
Nagendra Pedipina
7/13/2023 2:22:00 AM

q:42 there has to be a image in the question to choose what does it mean from the options

B
BrainDumpee
11/18/2023 1:36:00 PM

looking for cphq dumps, where can i find these for free? please and thank you.

S
sheik
10/14/2023 11:37:00 AM

@aarun , thanks for the information. it would be great help if you share your email

R
Random user
12/11/2023 1:34:00 AM

1z0-1078-23 need this dumps

L
labuschanka
11/16/2023 6:06:00 PM

i gave the microsoft azure az-500 tests and prepared from this site as it has latest mock tests available which helped me evaluate my performance and score 919/1000

M
Marianne
10/22/2023 11:57:00 PM

i cannot see the button to go to the questions

S
sushant
6/28/2023 4:52:00 AM

good questions

A
A\MAM
6/27/2023 5:17:00 PM

q-6 ans-b correct. https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-cli-quick-start/use-the-cli/commit-configuration-changes

AI Tutor 👋 I’m here to help!